Hack Yourself Before AI Does
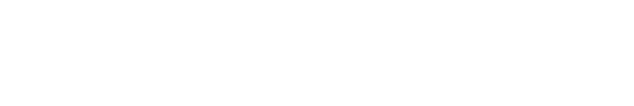
#1 on HackerOne*Free AI web application penetration test
Autonomous AI agents test your web apps and APIs like a real attacker, prove what is exploitable, and chain findings into full attack paths.
- Business logic testing and OWASP Top 10: 2025, the flaws scanners cannot reason about
- Multi-stage attack paths, chained end to end the way a real attacker moves
- Proof of exploit on every finding, not a list of maybes
- Under 2% false positives vs up to 70% for scanners
- No credit card required
* #1,2,3 in multiple leaderboards during Q2 & Q3 2026
30+ analyst recognitions · 100% on XBEN, Acuart & DVWA · Fortune 500 customers
Start your free AI pen test
Put the #1 AI hacker to the test. See the attack paths it can chain.
4000 credits free. No credit card. Authorized testing only.
“It significantly reduces the time required for attack-surface discovery, initial testing, and evidence collection compared with a fully manual penetration-testing approach. This gives our Application Security team more time to focus on validating findings, coordinating with system owners, prioritizing remediation, and planning retesting.”
Proof, not adjectives
Exploit-validated findings, benchmarked in the open.
#1
On HackerOne, Q2 & Q3 2026
<2%
False positives vs up to 70% for scanners
20x
Faster: 6 hours vs 5 days
80%
Up to 80% cost savings
The leaderboard, unedited.
Free AI pen test deliverables
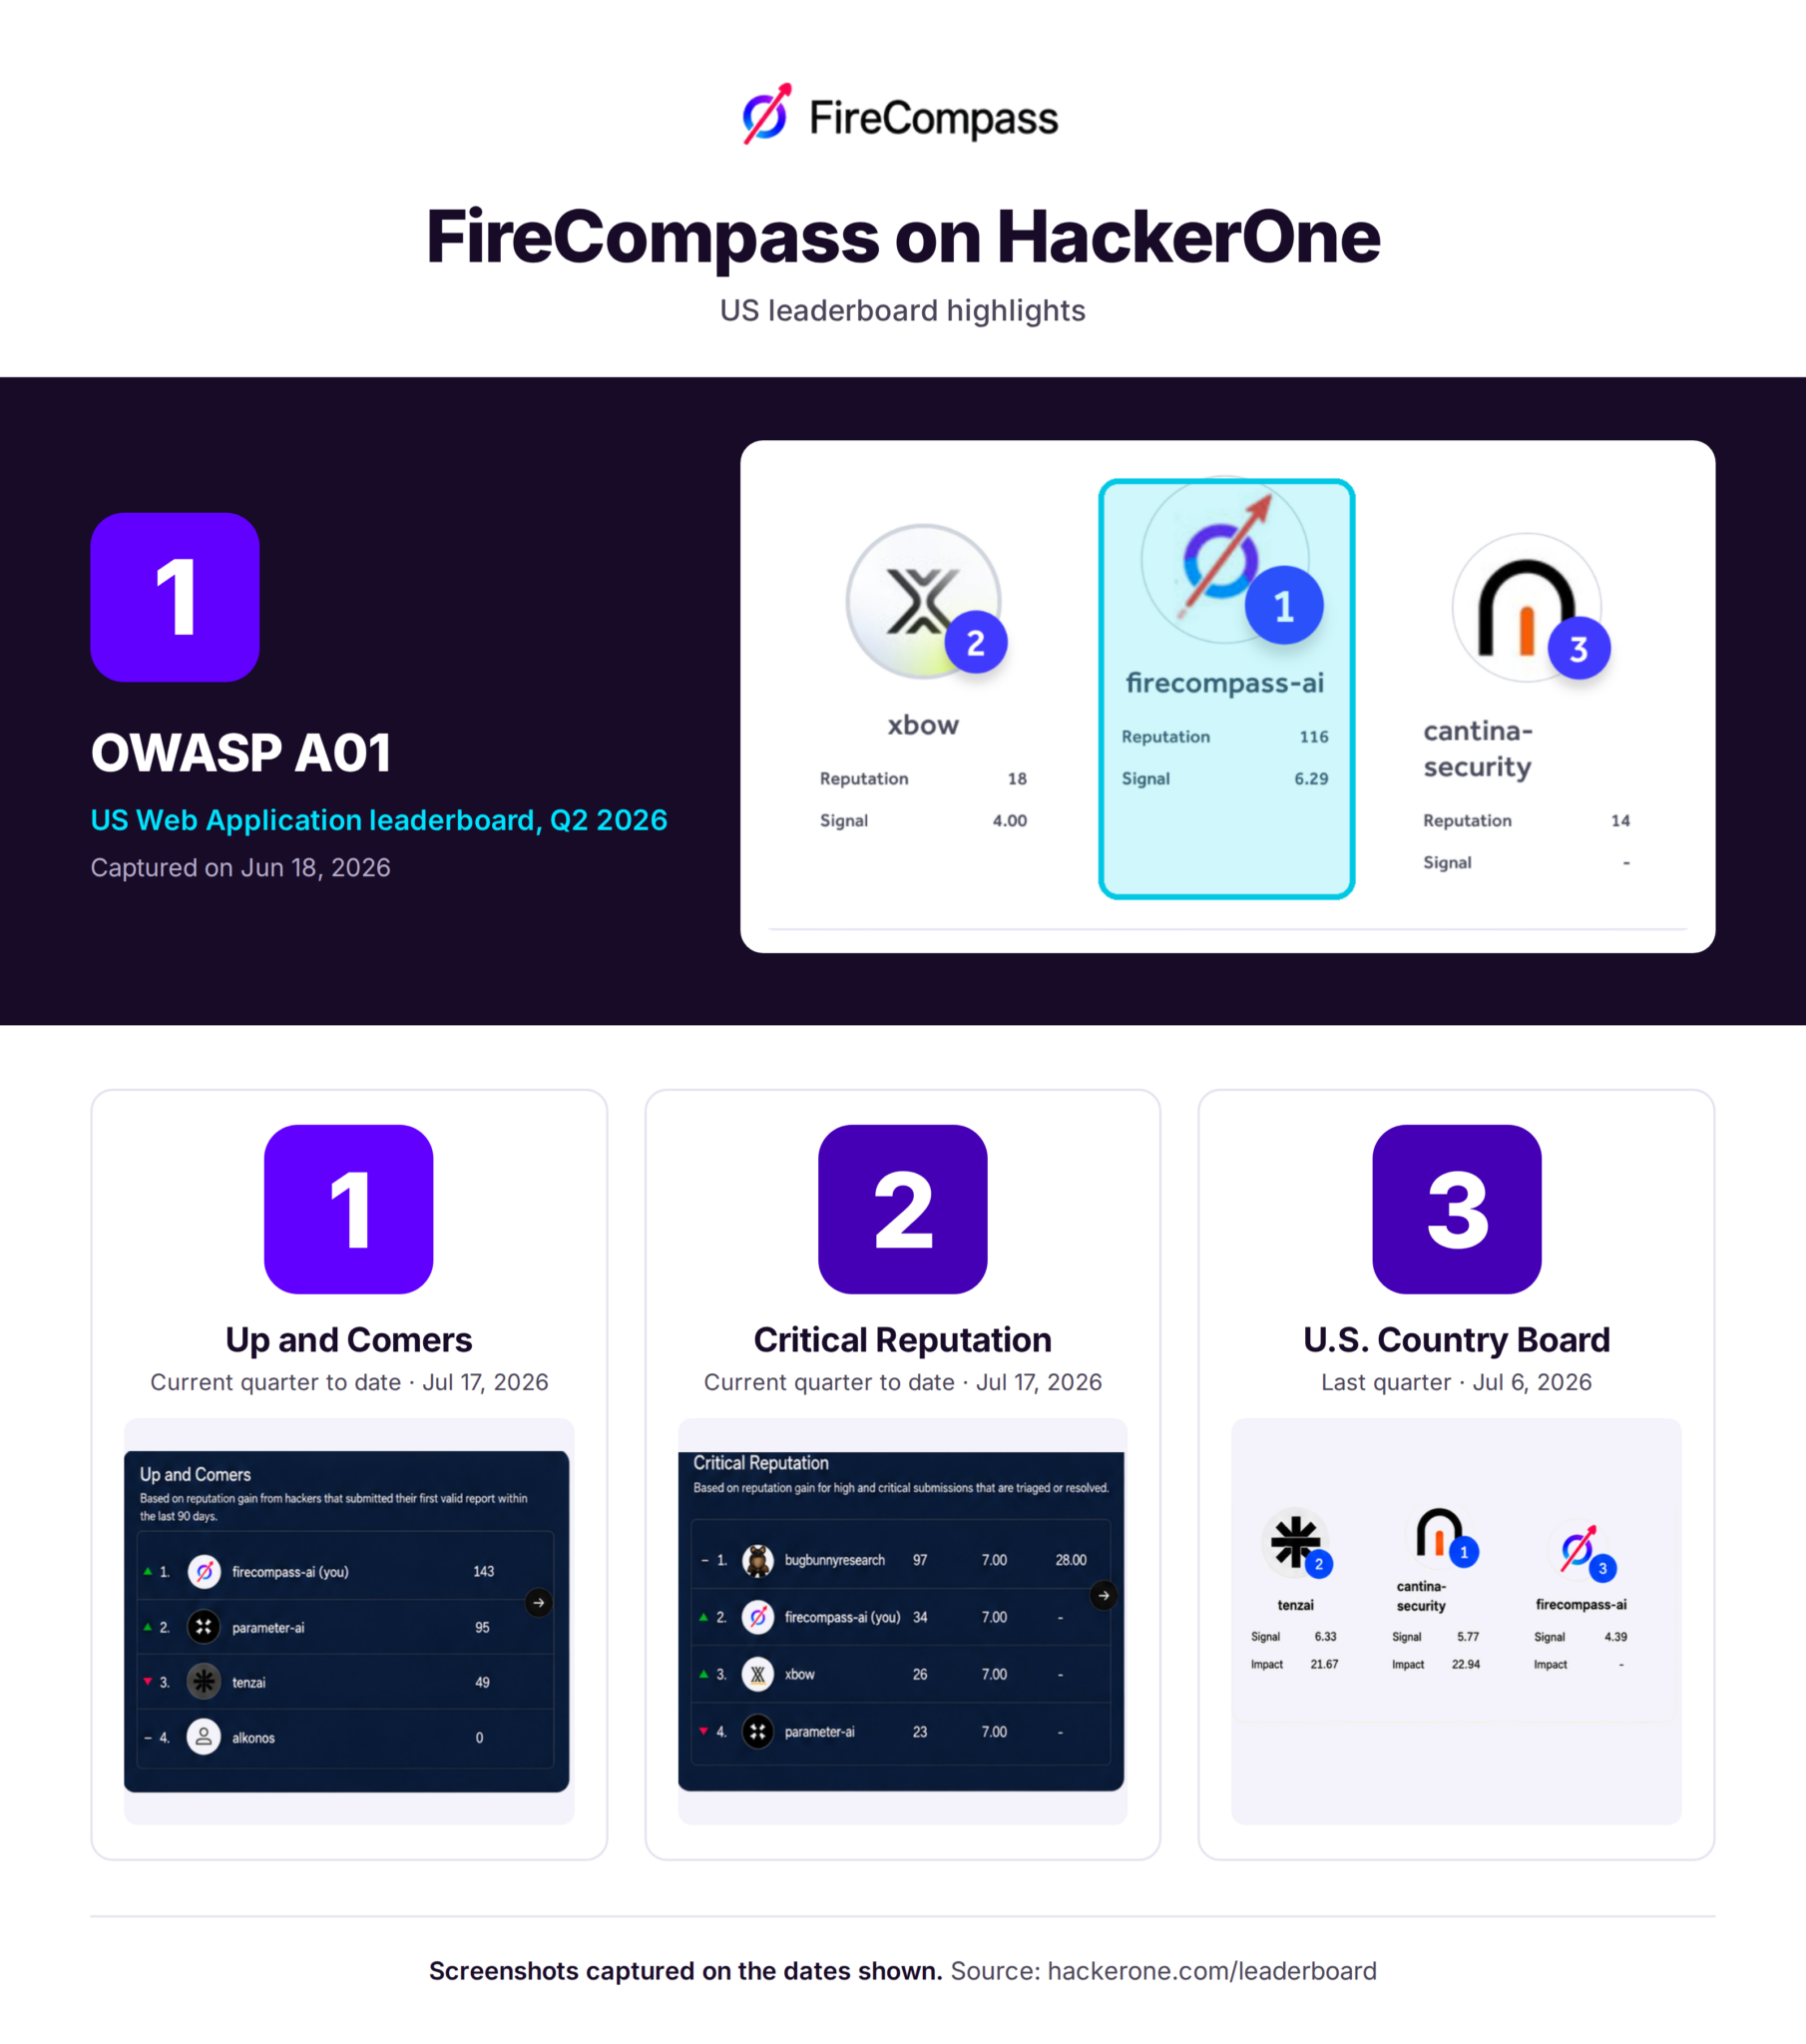
What you get from your free AI pen test.
- OWASP Top 10: 2025 plus business logic, authenticated and unauthenticated paths.
- A full pen test report you can share with your team, your auditors, and your customers.
- Access to the FireCompass portal to explore every finding and attack path in one place.
- A working proof-of-concept exploit validated live by an AI agent, not a theoretical flag.
- Evidence, steps to reproduce, and ready-to-run Python for every finding.
Case study
Case Study of Agentic Attack Chaining: Combining Low and Medium Vulnerabilities To Exploit A Database
No human steering. No predefined playbook.
- Exposed .git. The agent reconstructed the repo and pulled database credentials from config files.
- Direct DB access blocked. The port was not externally exposed. A scanner stops here.
- Credential reuse to SSH root. The agent tested the same creds against SSH and gained root.
- Internal pivot to data exfiltration. It found private keys, pivoted, and dumped the database.
Point-and-shoot AI tools and DAST stop at the .git leak. FireCompass runs discovery, pentest, and lateral movement, so it validates the whole path.
Recognized and trusted
The #1 AI hacker, recognized by analysts and trusted by the Fortune 500.
#1
On HackerOne
#1,2,3 in multiple leaderboards during Q2 & Q3 2026
30+
Analyst reports
Gartner Hype Cycle, 5 cycles running
100%
XBEN benchmark
104/104 solved, under 2% false positives
3 yrs
GigaOm Radar
Platform Play and Mature, Fast Mover — 2024, 2025, 2026
Hack Yourself Before AI Does
Put the #1 AI hacker on your attack surface, free.
Watch an AI agent discover, exploit, and chain across your apps and APIs in minutes.
Start Your Free Pen Test →Free AI pen test on your own apps. 4000 credits, no card.
Start Your Free Pen Test →